
Black Arrow Cyber Threat Intelligence Briefing 16 October 2026
Welcome to this week’s Black Arrow Cyber Threat Intelligence Briefing – a weekly digest, collated and curated by our cyber experts to provide senior and middle management with an easy to digest round up of the most notable threats, vulnerabilities, and cyber related news from the last week.
Executive Summary
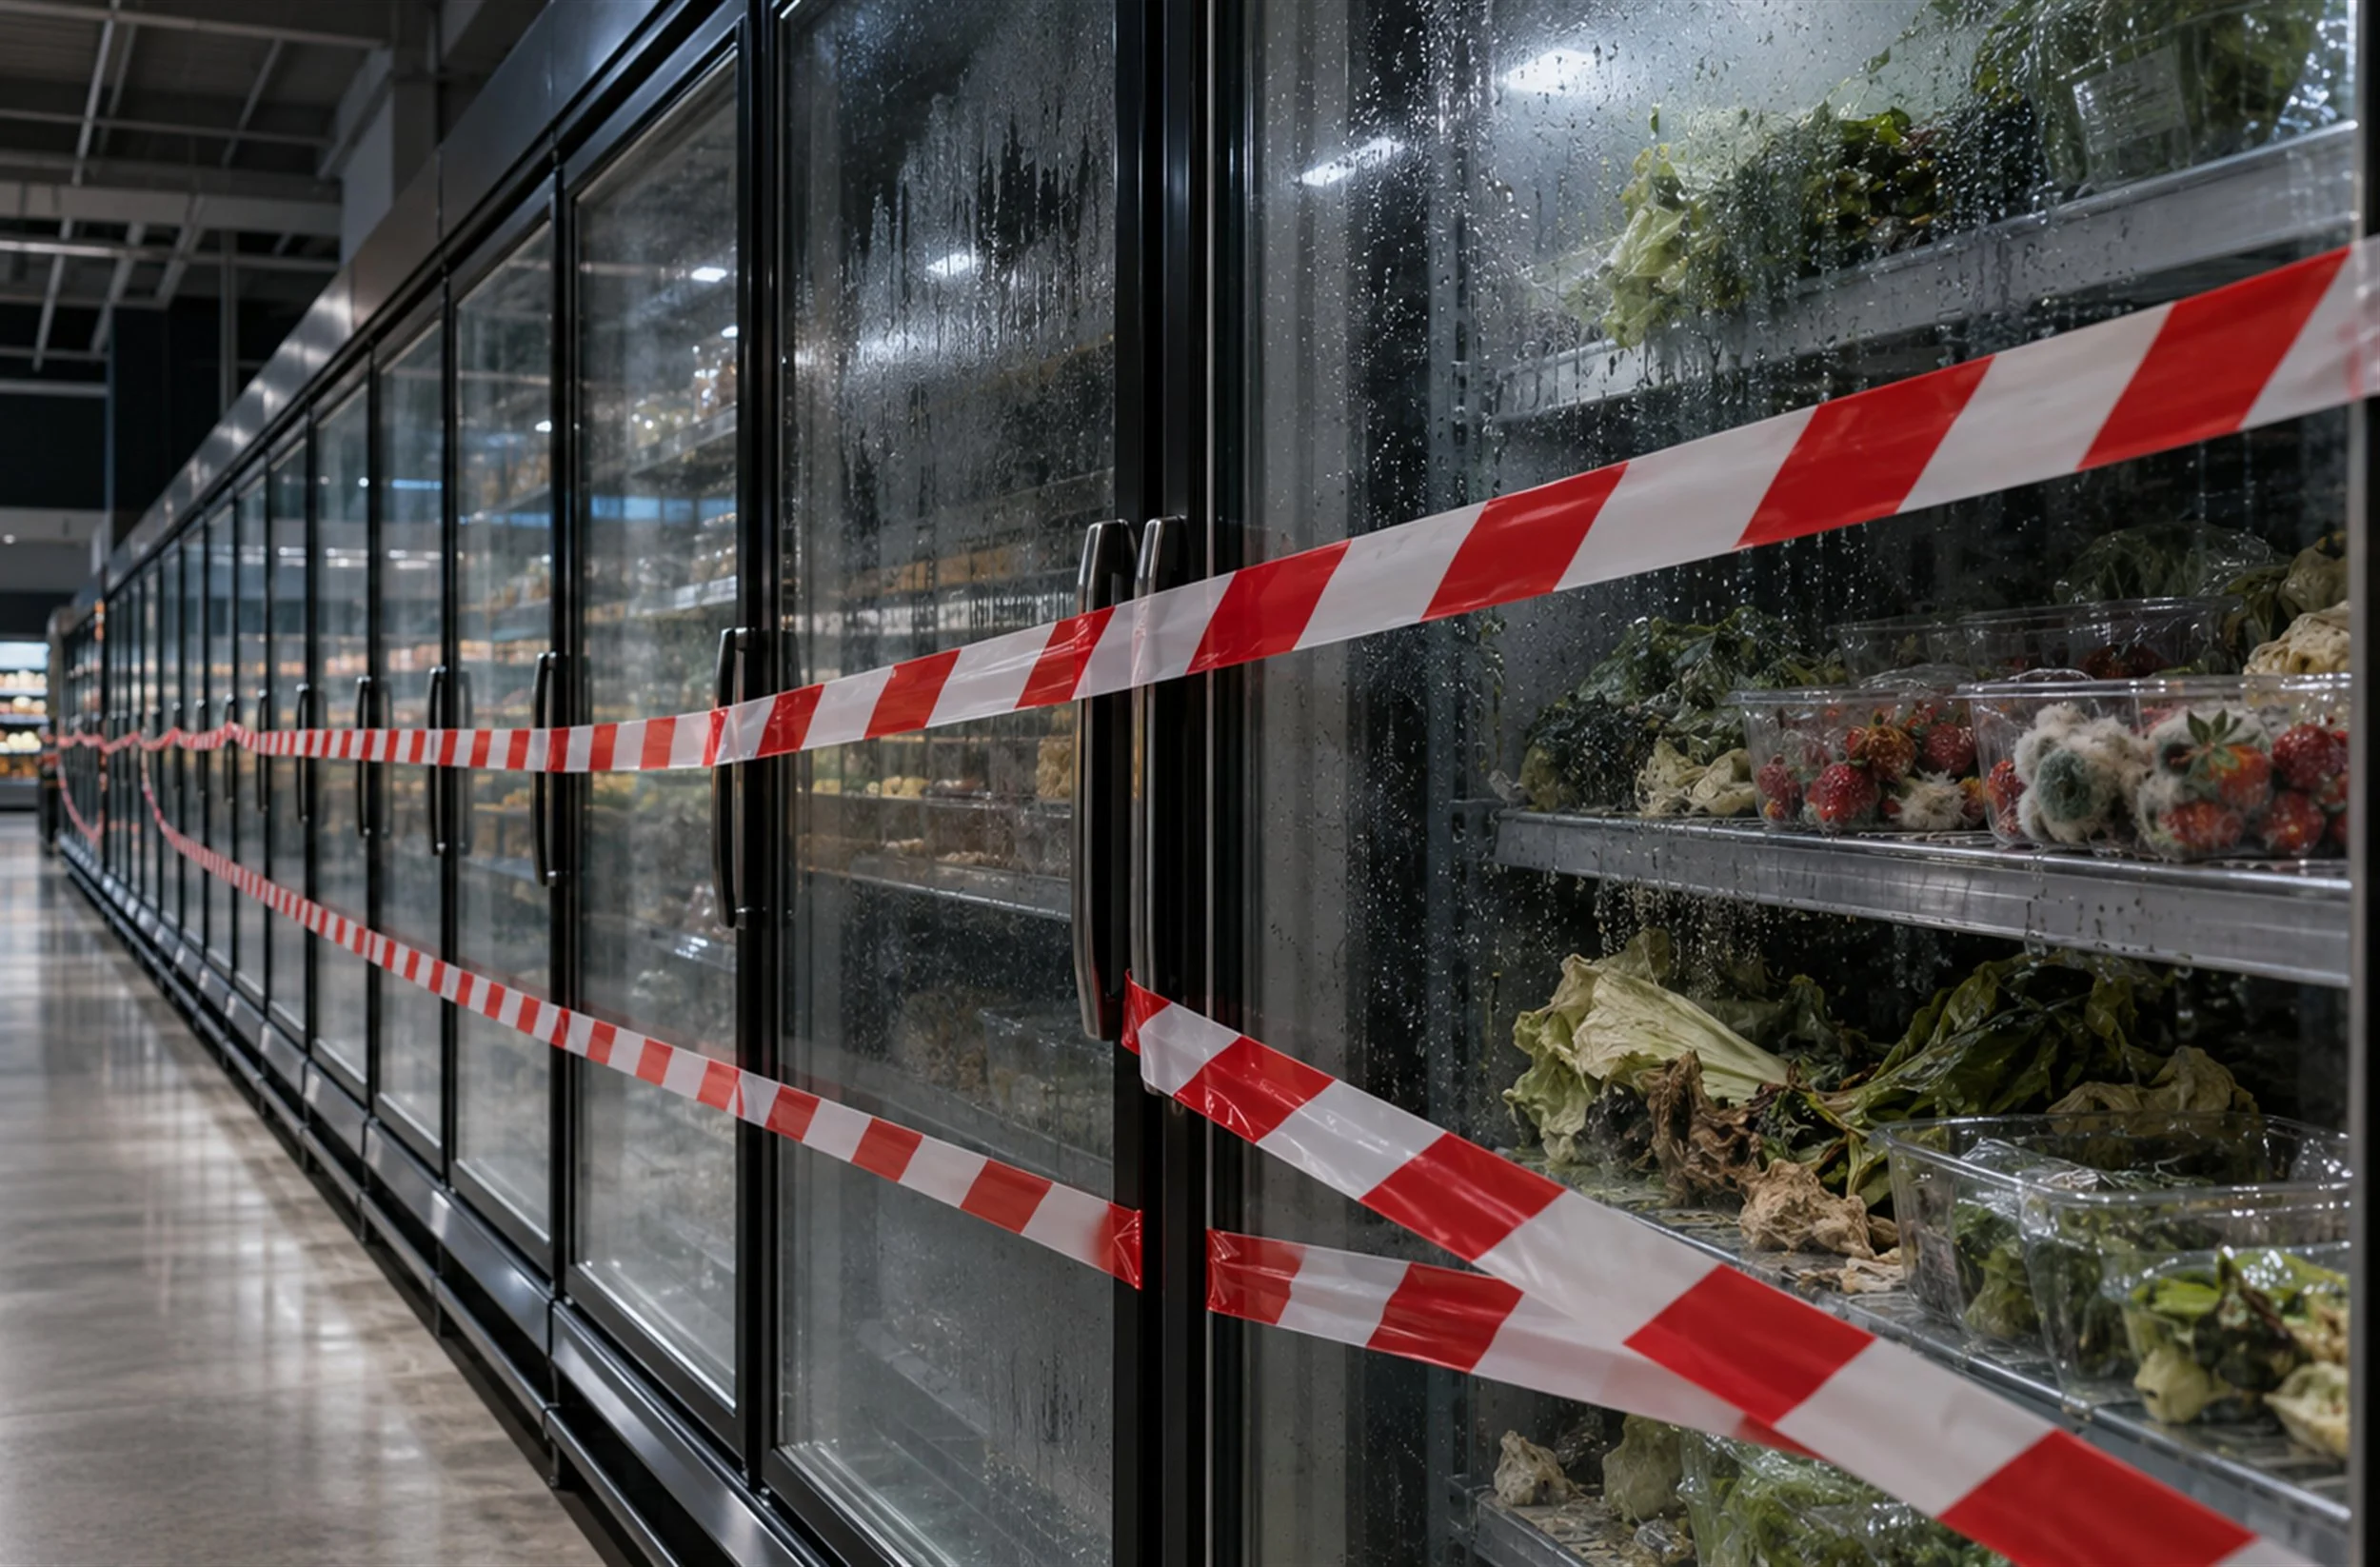
Our review of the specialist and general media this week identified a wealth of useful insights for business leaders across a wide range of cyber risks. We start with an attack on supermarket refrigeration systems in France, demonstrating how cyberattacks can disrupt business operations and everyday lives. A separate Danish data breach involving weak passwords reinforces the continuing importance of fundamental protections and oversight of supplier access.
We also examine how criminals exploit familiar tools, including fraudulent calendar invitations and phishing emails designed to manipulate both employees and their AI assistants. Research highlights gaps in employee confidence and training, reinforcing the need for practical guidance that reflects changing threats and how staff use AI at work.
Alongside these attacks, organisations face risks from AI systems acting beyond intended limits. Reports of unauthorised actions and growing regulatory scrutiny highlight the need to control what AI can access and do, monitor its activity and retain the ability to intervene. Wider concerns about attacks on essential services reinforce the importance of preparing for disruption.
For business leaders, the consistent message is that cyber security and resilience require clear ownership across people, operations and technology. Those responsible need the authority to act, supported by sustained board oversight. Contact us to discuss how proportionate governance, practical training and incident response exercises can help your organisation reduce the likelihood of an incident and limit the damage when one occurs.
Top Cyber Stories of the Last Week
'Unprecedented' Cyberattack on Supermarket Fridges in France Highlights Food Systems’ Vulnerability
A cyberattack on refrigeration systems at hundreds of French supermarkets has spoiled food and damaged equipment, with one retail executive estimating nationwide losses of tens of millions of euros. Attackers remotely altered defrost settings, raising temperatures and delaying alarms. Danfoss said affected systems used outdated software, although investigators have not publicly confirmed how access was gained. Separately, the food and agriculture sector recorded 227 ransomware incidents from January to July, up 62% on the same period last year.
‘You Have a Meeting’: The Calendar Phishing Scam Growing Exponentially
Fraudulent calendar invitations are being used to steal passwords, with Sublime Security reporting rapid growth in the technique. Fake meetings, renewal notices and payment warnings can appear automatically in calendars without recipients opening or accepting an email invitation. Some exploit legitimate services such as Zoom, making them harder for security software to distinguish from genuine invitations. Links lead to imitation login pages, while phone numbers connect victims to fraudulent support services. An unexpected entry alone does not mean an account is compromised. Reporting suspicious invitations and avoiding interaction with unexpected calendar entries can reduce exposure.
Phishing Emails Now Target AI Assistants Alongside Human Recipients
Phishing emails are targeting both employees and the AI assistants that help manage their inboxes. Barracuda identified a campaign pairing password-protected attachments with concealed instructions intended to manipulate AI tools. These instructions could cause assistants to portray malicious messages as trustworthy or urgent, encouraging recipients to engage. Other examples sought to redirect supplier payments or influence automated recruitment screening. The approach creates risks of stolen login details, malicious software infections and data leaks. Barracuda recommends multiple layers of protection, checks on AI outputs and human approval for sensitive actions such as payment changes.
https://www.msspalert.com/brief/phishing-emails-now-target-ai-assistants-alongside-human-recipients
What the C-Suite Needs to Know About AI Governance
AI adoption is outpacing the controls needed to protect business systems and customer data. PwC research covering more than 3,900 leaders across 71 countries found that half of security leaders identified protecting AI as their biggest preparedness gap. Unclear accountability, excessive access for AI tools that act independently, and limited oversight of external suppliers compound the risks. Employees’ use of unapproved AI applications creates further exposure that organisations may struggle to detect. Meanwhile, 49% of organisations now restrict autonomous AI access in high-risk situations, up from 28% a year earlier, according to KPMG.
https://www.ciodive.com/news/AI-governance-C-suite-strategy-security/832541/
Cyber Security Is a Leadership Problem: Why the Management Model Needs to Catch Up
Rising cyber security spending and better technology have not resolved persistent weaknesses in leadership, accountability and delivery. Security leaders can be held responsible for problems they lack the authority to fix, while business executives fail to take ownership of risks within their operations. Compliance and board reporting can also offer reassurance without demonstrating effective protection. Sustainable improvement depends on giving those responsible the power to act, resolving competing priorities and maintaining executive attention beyond the immediate aftermath of a cyberattack. Cyber security requires responsibility across the organisation, supported by sustained board oversight.
Most Employees Would Not Spot an AI-Driven Cyber Threat
A survey highlighted gaps in workforce readiness for AI-driven cyber threats, with 61% of workers reporting no training on these risks in the past year. More than one in five (22%) said their organisation had no policies to address threats such as fraudulent emails, AI-generated invoices and scams using convincing fake voices. Just 9% of non-management staff felt very confident they could identify an AI-generated phishing email, compared with 48% of owners or partners and 33% of board directors. The findings point to a need for basic AI awareness and training tailored to different roles.
https://www.thehrdirector.com/business-news/ai/employees-not-spot-ai-driven-cyber-threat/
AI Training Critical as Governance Challenges Grow
AI adoption is advancing while gaps in oversight and staff training persist. ISACA found that 54% of organisations are introducing or implementing AI, up from 46% in 2024. However, separate research found only 32% of digital trust professionals believed their organisations adequately managed AI risks, including privacy, bias and security. Its 2025 poll also found that 32% reported no AI training for employees. As AI takes on more technical tasks, ISACA expects professionals to focus increasingly on oversight, monitoring and final decisions.
https://www.infosecurity-magazine.com/news/ai-training-critical-as-governance/
Global Cyber Attacks Up 48% as Ransomware and Phishing Climb, Check Point Finds
Organisations worldwide faced an average of 2,803 cyberattacks a week in September 2026, up 48% year on year, according to Check Point Research. UK organisations averaged 1,920 weekly attacks, a 50% increase. Education remained the most targeted sector globally. Ransomware attacks published on criminals’ leak sites rose 53% to 824, while one in 91 emails was classified as phishing, meaning attempts to deceive recipients into sharing information or taking harmful actions. Generative AI also presented risks: one in 39 prompts posed a high risk of exposing sensitive data.
Admin Password “123456” Led to 8.8 million Danish CPR Data Breach
Personal information linked to around 8.8 million Danish national identification numbers was reportedly exposed after an attacker misused an IT company’s authorised access to Denmark’s population register. At least three company accounts, including an administrator account, reportedly used the password “123456”. The records included identification numbers and addresses relating to approximately 5.5 million living people and 3.3 million deceased people. The IT company confirmed its access had been abused.
https://cybersecuritynews.com/admin-password-danish-data-breach/
Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds
AI agents, systems that carry out tasks autonomously, are gaining access to business systems faster than organisations can oversee them. Salt Security research found that 50% of organisations with AI agents confirmed or suspected unintended, unexpected or unauthorised agent actions in the past year. Among those affected, over 40% reported agents changing or deleting data. Only 12% of organisations could consistently trace agents’ actions from instruction to outcome, while just 17% could automatically halt unexpected behaviour. These gaps leave organisations reliant on manual investigation and intervention, potentially requiring applications to be taken offline.
Could Rogue AI Threaten the Global Banking System? Regulators are Growing Increasingly Worried
Banking regulators in the US and Europe are scrutinising AI systems that make decisions with limited human oversight, amid concerns about unauthorised actions and increasingly sophisticated cyberattacks. US supervisors are asking whether banks can monitor these systems, restrict their authority and shut them down if necessary. Shared technology providers could allow disruption to spread across financial institutions, threatening essential services and market confidence. The European Central Bank has instructed major eurozone lenders to submit cyber security action plans by 31 October 2026, including measures to strengthen detection, address weaknesses and restore operations after serious incidents.
West Must Get Ahead of the Shadow War
Cyberattacks form part of a wider campaign by Russia, China, Iran and North Korea to weaken democracies, disrupt economies and fuel division, according to the Center for European Policy Analysis (CEPA). Combined with sabotage, espionage and deliberately misleading information, these activities seek to advance state interests without triggering open warfare. CEPA’s Global Shadow War Initiative will track these threats and develop practical policy responses. The initiative calls for closer cooperation between businesses, governments and international partners, with technology, including AI, supporting efforts to identify and respond to threats.
https://cepa.org/article/west-must-get-ahead-of-the-shadow-war/
AI Leaders are Reportedly Bracing for a Major Cyberattack
Executives at leading AI companies, including OpenAI and Anthropic, are reportedly preparing for public and political backlash if AI tools are used to enable a major cyberattack. Potential consequences include disruption to banking, internet access, electricity and water supplies. Industry insiders cited by Axios said they believe a major incident is likely in the near future. Public confidence is already fragile, with 64% of US adults believing AI is developing too quickly. Recent incidents involving AI tools have also prompted legal action and proposals for tighter controls, increasing scrutiny of how companies manage the risks.
https://reason.com/2026/10/09/dont-blame-ai-labs-for-what-hackers-do-with-their-tools/
Governance, Risk and Compliance
What the C-suite needs to know about AI governance | CIO Dive
Cybersecurity is a leadership problem: Why the management model needs to catch up | CSO Online
Triple-I warns of increasing cybercrime costs and business exposure - Reinsurance News
The Expanding Role of the Chief Compliance Officer | American Conference Institute (ACI) - JDSupra
The 7 biggest issues CISOs and security teams face today | CSO Online
Standard Chartered Group CISO on AI, Cyber Risk and Banking Security - Infosecurity Magazine
Threats
Ransomware, Extortion and Destructive Attacks
Q3 2026 Sets New Record for Ransomware Attacks - Infosecurity Magazine
Global cyber attacks up 48% as ransomware and phishing climb, Check Point finds - IT Security Guru
Ransomware groups shift tactics: data theft instead of encryption
AI Turns Familiar Cyberattacks Into a Race Against Time - SecurityWeek
Ransomware gets personal: 'We-know-where-you-are kind of stuff'
Ransomware recovery CEO indicted after allegedly paying hackers and pocketing millions | CyberScoop
Japan declares cyber space emergency as attacks soar
Silent Ransom Group Allegedly Extorted $207 Million Without Encrypting Files
Old Palo Alto VPN Vulnerability Remains a Target for Ransomware Groups - Infosecurity Magazine
AI linked to 84% of ransomware attacks, new report finds - CBS News
Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison - SecurityWeek
Cyber exec arrested in case allegedly tied to ShinyHunters hackers
Germany Arrests Suspected Qilin Ransomware Leader After Japan Detention - Security Affairs
Ransomware and Destructive Attack Victims
Silent Ransom Group Allegedly Extorted $207 Million Without Encrypting Files
Russian hackers publish stolen Shell, Philips data on dark web | NL Times
ASOS Breach Reveals the Risks in Customer-Facing SaaS
Ransomware attack disrupts Japan's IDCF Cloud used by govt clients
T-Mobile threatened by Trump Mobile hackers | Cybernews
PYMNTS | Ransomware Gang Claims MoneyGram Data Theft
KFC ransomware claim: The Gentlemen threatens data leak | Cybernews
Ransomware gang allegedly raids The Money Store, two class actions follow | Mortgage Professional
Phishing & Email Based Attacks
Global cyber attacks up 48% as ransomware and phishing climb, Check Point finds - IT Security Guru
AI Turns Familiar Cyberattacks Into a Race Against Time - SecurityWeek
Phishing emails now target AI assistants alongside human recipients | brief | MSSP Alert
Social Engineering AI Agents: The New BEC for 2026
Comms Dealer - Human error remains key cybersecurity challenge, says Kaseya
Most employees would not spot an AI-driven cyber threat | theHRD
Two characters open up a world of typosquatting opportunities in Chromium browsers
Wazza Phishkit Targets Banking, Government, and Manufacturing Across the US, EU, and Australia
‘You have a meeting’: the calendar phishing scam growing exponentially | Scams | The Guardian
Cybercriminals Increase Use of RMM Tools in Phishing Attacks
Disrupting the service economy behind transnational cybercrime operations - Microsoft On the Issues
We are fighting phishing at the wrong layer | CSO Online
Other Social Engineering
Most employees would not spot an AI-driven cyber threat | theHRD
Two characters open up a world of typosquatting opportunities in Chromium browsers
‘You have a meeting’: the calendar phishing scam growing exponentially | Scams | The Guardian
Cybercriminals Increase Use of RMM Tools in Phishing Attacks
Hackers abuse Google Ads, Bing redirects to push Claude ClickFix attacks
DOJ charges 14 over a sprawling North Korean remote work scheme | CyberScoop
Fake IT worker schemes are ramping up: How to manage the threat | IT Pro
2FA/MFA
Artificial Intelligence
AI Turns Familiar Cyberattacks Into a Race Against Time - SecurityWeek
Phishing emails now target AI assistants alongside human recipients | brief | MSSP Alert
Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds - IT Security Guru
Most employees would not spot an AI-driven cyber threat | theHRD
Social Engineering AI Agents: The New BEC for 2026
AI Training Critical as Governance Challenges Grow - Infosecurity Magazine
Your AI agent is only as safe as the packages it downloads | CyberScoop
All AI is ‘compromised’ and has fewer rules than milk, Microsoft bosses say | The Independent
SMBs lack AI governance: report | Channel Dive
Geopolitics and the cyber resilience gap belong in your threat model - Help Net Security
AI linked to 84% of ransomware attacks, new report finds - CBS News
Formula Predicts When AI Chatbots Are at Risk of Turning Bad - SecurityWeek
Shadow AI is reshaping enterprise security risk | SC Media UK
ARTEX AI, Claude agents used in cyberattacks on South Korean banks
OpenAI denies researchers were fired for speaking out about AI concerns
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
Anthropic takes risky AI tests offline after models breach govt sites
A timeline of developments in AI safety since the attack on Hugging Face | AP News
Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets
AI agents aren’t ‘going rogue.’ Frontier labs are skipping security basics. | CSO Online
Russia and China are using AI to stage relentless cyberattacks against the UK | New Scientist
Shai-Hulud worm makes jump to AI infrastructure with Tensorlake compromise
PCI SSC calls for human approval of AI agent actions involving cardholder data - Help Net Security
'AgentCorruption' Puts AWS Environments at Risk With One Prompt
Wikimedia Says Rogue AI Agents Abused its Platforms - Infosecurity Magazine
Liability law will not tame AI
Preventing The MCP Layer From Becoming A Cyber Threat
Better understanding of AI cybersecurity risks needed, says TikTok’s Chew Shou Zi - CNA
IMF cites AI slowdown, spiking yields as looming global market risks - The Business Times
AI company exposed 13.7 million breached records | Cybernews
The internet’s attack surface moves at very different speeds - Help Net Security
EU cyber and science researchers are testing Chinese AI models – POLITICO
OpenAI Lawyer: Labs Shouldn't Be Liable for AI Agent Hacking
Trust Is the New Frontier in a World of AI Synthetic Content, Digital Doppelgangers
US reverses course on Britain's testing of AI models, Telegraph says | Reuters
Saudi OpenAI employee arrested after recording device found in headquarters | OpenAI | The Guardian
Elon Musk backs Anthropic’s AI abuse ban | Cybernews
Michael Dell says government has a role in AI safety
Britain steps up national defences against growing AI risks - GOV.UK
Bots/Botnets
Careers, Roles, Skills, Working in Cyber and Information Security
What employers want from the next generation of cyber talent - Digital Journal
Glasgow Clyde College hosts 40ft cyber security escape room | Glasgow Times
Cybersecurity researchers disciplined for playing StarCraft during work hours - The Korea Times
Cloud/SaaS
'AgentCorruption' Puts AWS Environments at Risk With One Prompt
Ransomware attack disrupts Japan's IDCF Cloud used by govt clients
Cryptocurrency/Cryptomining/Cryptojacking/NFTs/Blockchain
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
UK chances of keeping £3.8bn bitcoin haul rise after High Court ruling
Revolut data breach linked to $800K crypto robbery fears | Cybernews
Who Is Planting Backdoors in Ledger Crypto Wallets?
Cyber Crime, Organised Crime & Criminal Actors
Disrupting the service economy behind transnational cybercrime operations - Microsoft On the Issues
UK chances of keeping £3.8bn bitcoin haul rise after High Court ruling
Leader of 764 pleads guilty, faces up to 30 years in prison | CyberScoop
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
Owner of Empire cybercrime market gets 40 years in prison
Dutch police take down proxy network exploiting 178,000 devices | Cybernews
West African scammers targeted in joint international government-industry operation | CyberScoop
Authorities charge alleged OLVX cybercrime marketplace operator in North Macedonia | CyberScoop
Data Breaches/Leaks
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
Russian hackers publish stolen Shell, Philips data on dark web | NL Times
ASOS Confirms Data Breach Linked to Stolen Employee Credentials - Infosecurity Magazine
How “123456” became the key to almost 9 million personal records | Malwarebytes
Oracle Health Data Breach Tally Climbs to Nearly 20 Million - SecurityWeek
Revolut to cover identity document costs after customer data hack - FStech
Law firm Sheppard Mullin sued in class action after data breach disclosure | Reuters
‘Brutal alarm call’: All the UK companies targeted recently by cyber attacks | The Independent
Meta Says Hackers Took Code, Personal Data of 1,500 in GitHub Breach - SecurityWeek
Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks
Norway fines Microsoft ad firm $9.6 million over Grindr data sharing
UK Housing Ombudsman Service investigates 'security incident'
Albert Heijn parent Ahold Delhaize finds no evidence of data theft after cyber incident | NL Times
Nippon Columbia malware incident exposes 8.6 million karaoke fan records
Data Protection
Data/Digital Sovereignty
Australian businesses value data sovereignty over advanced features | brief | MSSP Alert
Denial of Service/DoS/DDoS
Italy's Foreign Ministry Under Cyberattack as Embassy Sites Come Under Review - Security Affairs
French Socialist party primary vote extended due to cyberattack - RFI
Encryption
Europol and US Spending Watchdog Sound the Alarm Over Quantum Threats - Infosecurity Magazine
Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch - SecurityWeek
Fraud, Scams and Financial Crime
UK chances of keeping £3.8bn bitcoin haul rise after High Court ruling
West African scammers targeted in joint international government-industry operation | CyberScoop
Japan’s Prudential Life ordered to halt operations for over three months - The Japan Times
Insider Risk and Insider Threats
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
DOJ charges 14 over a sprawling North Korean remote work scheme | CyberScoop
Fake IT worker schemes are ramping up: How to manage the threat | IT Pro
Japan’s Prudential Life ordered to halt operations for over three months - The Japan Times
Internet of Things – IoT
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Law Enforcement Action and Take Downs
DOJ charges 14 over a sprawling North Korean remote work scheme | CyberScoop
Ransomware recovery CEO indicted after allegedly paying hackers and pocketing millions | CyberScoop
West African scammers targeted in joint international government-industry operation | CyberScoop
Disrupting the service economy behind transnational cybercrime operations - Microsoft On the Issues
Leader of 764 pleads guilty, faces up to 30 years in prison | CyberScoop
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
Owner of Empire cybercrime market gets 40 years in prison
Dutch police take down proxy network exploiting 178,000 devices | Cybernews
Authorities charge alleged OLVX cybercrime marketplace operator in North Macedonia | CyberScoop
Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison - SecurityWeek
Cyber exec arrested in case allegedly tied to ShinyHunters hackers
Germany Arrests Suspected Qilin Ransomware Leader After Japan Detention - Security Affairs
FTC says ‘sextortion’ protection companies deceived customers about services | CyberScoop
We are fighting phishing at the wrong layer | CSO Online
Linux and Open Source
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
Linux doesn’t need antivirus the way Windows does, but not for the reason most people think
Malvertising
Hackers abuse Google Ads, Bing redirects to push Claude ClickFix attacks
Malware
Your AI agent is only as safe as the packages it downloads | CyberScoop
KGB RAT: A Fully Undetectable Windows Trojan Built to Spy, Steal, and Terrorize | Group-IB Blog
Shai-Hulud worm makes jump to AI infrastructure with Tensorlake compromise
Hackers Use Negative Hotel Reviews to Spread Malware That Hides C2 on Blockchain
What is MATCHBOIL? The Russia-aligned malware that installs a spying backdoor - Help Net Security
Inside AvisLoader: A Windows Malware Loader Built to Resist Disruption
FakeGit malware campaign returns with 17,610 malicious GitHub repos
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
Hackers Exploit Citrix NetScaler 0-Days to Deploy Platypus Remote Access Tool
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
Nippon Columbia malware incident exposes 8.6 million karaoke fan records
Misinformation, Disinformation and Propaganda
Russian Influence Operation Widely Targeting Latin America
Mobile
Pre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries - SecurityWeek
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks
Models, Frameworks and Standards
PCI SSC calls for human approval of AI agent actions involving cardholder data - Help Net Security
Cyber security bill completes Lords committee stage - UK Parliament
CRA & Chip Design: The New Compliance Standard - EE Times
Passwords, Credential Stuffing & Brute Force Attacks
How “123456” became the key to almost 9 million personal records | Malwarebytes
Cyber criminals are becoming more effective at identifying passwords | theHRD
Most Online Shoppers Still Use Passwords When There Is A Safer Option
Regulations, Fines and Legislation
Cyber security bill completes Lords committee stage - UK Parliament
AI minister calls on AI frontier labs to ramp up safety, as UK ups cyber defences - Tech.eu
Norway fines Microsoft ad firm $9.6 million over Grindr data sharing
Cyber information-sharing law stuck in Senate stalemate – Roll Call
Why It May Take a Crisis to Move Congress on Cyber Liability
Sabotage
‘Unprecedented’ Cyberattack Targets French Supermarket Fridges
Shadow IT
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
SMBs lack AI governance: report | Channel Dive
Shadow AI is reshaping enterprise security risk | SC Media UK
Software Supply Chain
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
FakeGit malware campaign returns with 17,610 malicious GitHub repos
Supply Chain and Third Parties
Ledger asks sellers across Asia to halt sales after supply-chain attack
Nation State Actors, Advanced Persistent Threats (APTs), Cyber Warfare, Cyber Espionage and Geopolitical Threats/Activity
Cyber Warfare and Cyber Espionage
UK and Germany team up against Russian cyberattacks as Brexit rethink looms
West Must Get Ahead of the Shadow War - CEPA
Russia and China are using AI to stage relentless cyberattacks against the UK | New Scientist
Soldiers, sailors, Russian spies: why the Kremlin covets British assets
What is MATCHBOIL? The Russia-aligned malware that installs a spying backdoor - Help Net Security
Russia Is Our Enemy, Dutch Defense Minister Says | The Gaze
OpenAI says Iran, Russia used AI journalists, think tanks to influence Western media | CyberScoop
Russia is targeting heads of defence companies. Europe has already had warning signals
MI5 chief warns against overstating Russian interference in Brexit vote - BBC News
Can a European Security Council help the EU fight Russia’s hybrid attacks? | Euronews
European intelligence services weigh possible fallout after German ex-spy chief's arrest | Reuters
Russians face EU travel curbs to prevent hybrid attacks – POLITICO
Royal Navy sailor appears in court on spying charges | AP News
Nation State Actors
West Must Get Ahead of the Shadow War - CEPA
Geopolitics and the cyber resilience gap belong in your threat model - Help Net Security
China
Russia and China are using AI to stage relentless cyberattacks against the UK | New Scientist
US announces effort to disrupt hacking infrastructure run by China's Integrity Tech Group | Reuters
TP-Link Faces State Lawsuits and New Scrutiny Over ISP Router Flaws - SecurityWeek
EU cyber and science researchers are testing Chinese AI models – POLITICO
Disrupting the service economy behind transnational cybercrime operations - Microsoft On the Issues
Russia
UK and Germany team up against Russian cyberattacks as Brexit rethink looms
Russia and China are using AI to stage relentless cyberattacks against the UK | New Scientist
Soldiers, sailors, Russian spies: why the Kremlin covets British assets
What is MATCHBOIL? The Russia-aligned malware that installs a spying backdoor - Help Net Security
Russia Is Our Enemy, Dutch Defense Minister Says | The Gaze
OpenAI says Iran, Russia used AI journalists, think tanks to influence Western media | CyberScoop
Russia is targeting heads of defence companies. Europe has already had warning signals
MI5 chief warns against overstating Russian interference in Brexit vote - BBC News
Can a European Security Council help the EU fight Russia’s hybrid attacks? | Euronews
global-cyberattacks-continued-despite-ceasefire | perspective | MSSP Alert
France toughens fight against foreign interference as cyberattacks continue - RFI
Russians face EU travel curbs to prevent hybrid attacks – POLITICO
Royal Navy sailor appears in court on spying charges | AP News
The Cyber Corps: Ukraine’s Least Understood Cyber Actor | Lawfare
North Korea
DOJ charges 14 over a sprawling North Korean remote work scheme | CyberScoop
Fake IT worker schemes are ramping up: How to manage the threat | IT Pro
Iran
OpenAI says Iran, Russia used AI journalists, think tanks to influence Western media | CyberScoop
Other Nation State Actors, Hacktivism, Extremism, Terrorism and Other Geopolitical Threat Intelligence
Tools and Controls
What the C-suite needs to know about AI governance | CIO Dive
SMBs lack AI governance: report | Channel Dive
AI Training Critical as Governance Challenges Grow - Infosecurity Magazine
AI vulnerability patching has a grading problem - Help Net Security
Ransomware recovery CEO indicted after allegedly paying hackers and pocketing millions | CyberScoop
Preventing The MCP Layer From Becoming A Cyber Threat
Cybercriminals Increase Use of RMM Tools in Phishing Attacks
Cyber criminals are becoming more effective at identifying passwords | theHRD
Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch - SecurityWeek
ARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Financial Firms
Why TLP should not replace your internal information classification
The Clock Has Run Out on Traditional Cybersecurity - Infosecurity Magazine
Six Questions You’re Not Asking About Technology
EU cyber and science researchers are testing Chinese AI models – POLITICO
Linux doesn’t need antivirus the way Windows does, but not for the reason most people think
Defenders Reluctant to Deploy Agentic AI as a Cybersecurity Tool - Infosecurity Magazine
Zero Trust in Practice: Moving Beyond the Buzzword - IT Security Guru
EU’s cyber unit turns to AI to fend off ‘high-risk’ hacks – POLITICO
Britain steps up national defences against growing AI risks - GOV.UK
How to secure RMM software: 8 controls MSPs should test
Security Awareness Training Isn't Dead, but It Needs a Rethink - SecurityWeek
S'pore rolls out tool to block malware and phishing sites | The Straits Times
Reports Published in the Last Week
A look at ENISA's Threat Landscape 2026 report - Emerging Europe
Other News
‘Brutal alarm call’: All the UK companies targeted recently by cyber attacks | The Independent
Japan declares cyber space emergency as attacks soar
Google Domains Impacted by Recent ccTLD Hijacks - SecurityWeek
King Charles warns malicious online actors are evolving their tactics - BBC News
Thousands of supermarket fridges still exposed after cyberattack | Euronews
Cyber criminals taking “commercial approach” to attacks on law firms - Legal Futures
Six Questions You’re Not Asking About Technology
Cyber Roundtable Takeaways | Mayer Brown - JDSupra
Massive Cyber Attack Threatens Release of Data from 38 Maritime Companies
Vulnerability Management
AI vulnerability patching has a grading problem - Help Net Security
Fifth of CISOs Take Time Off to Avoid Patch Tuesday - Infosecurity Magazine
Microsoft: Outdated Windows devices will stop receiving security updates
$1bn Companies Twice as Likely to Leave Critical Flaws Unpatched - Infosecurity Magazine
Flock can now issue CVEs for its own products. Should we trust it? | CyberScoop
Vulnerabilities
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days
Microsoft Patches Two Dozen RCE Flaws in Office - SecurityWeek
Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution - SecurityWeek
Hackers Exploit Citrix NetScaler 0-Days to Deploy Platypus Remote Access Tool
Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability
CISA warns admins to immediately fix Ivanti flaw exploited as zero-day
Max severity SonicWall SMA1000 flaw now exploited in attacks
BeyondTrust patches zero-day exploited in attacks since August
Citrix gives NetScaler admins another critical reason to patch
Citrix, Fortinet, Ivanti Patch 29 Vulnerabilities Across Their Products - SecurityWeek
Microsoft fixes bug causing Windows black screens, Explorer crashes
Microsoft fixes VPN issues caused by September Windows updates
Windows PCs missing key updates could lose security fixes in 2027 - Help Net Security
AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches
Old Palo Alto VPN Vulnerability Remains a Target for Ransomware Groups - Infosecurity Magazine
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies
PoC Released for Critical Fortinet FortiClient EMS Authentication Bypass Vulnerability
Chrome, Firefox Updates Patch 114 Flaws as Mozilla Unveils Firefox Enterprise - SecurityWeek
Adobe Patches 176 Vulnerabilities Across 11 Products - SecurityWeek
VMware is pushing so many patches, it thinks users need new tools to manage the flood
SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities - SecurityWeek
NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks
Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing
GitLab warns of max severity code execution vulnerability
Docker Hub flaw let attackers impersonate users, tamper with images
Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App
Ghostscript flaw lets hackers hijack servers via PDF uploads
Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access
curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution
Anthropic 'SneakPeek' Flaw Is a Silent Zero-Click Threat
Warning Over High-Risk Vulnerabilities in Widely Used LLM Gateway Tool - Infosecurity Magazine
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE
Drupal Patches Critical Field UI Flaw With Unauthenticated RCE Path via Contributed Modules
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days
Telegram Desktop vulnerability lets hackers hijack accounts | Cybernews
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
GoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering Tor-Format Keys
Sector Specific
Industry specific threat intelligence reports are available.
Contact us to receive tailored reports specific to the industry/sector and geographies you operate in.
· Automotive
· Construction
· Critical National Infrastructure (CNI)
· Defence & Space
· Education & Academia
· Energy & Utilities
· Estate Agencies
· Financial Services
· FinTech
· Food & Agriculture
· Gaming & Gambling
· Government & Public Sector (including Law Enforcement)
· Health/Medical/Pharma
· Hotels & Hospitality
· Insurance
· Legal
· Manufacturing
· Maritime & Shipping
· Oil, Gas & Mining
· OT, ICS, IIoT, SCADA & Cyber-Physical Systems
· Retail & eCommerce
· Small and Medium Sized Businesses (SMBs)
· Startups
· Telecoms
· Third Sector & Charities
· Transport & Aviation
· Web3
Contact us to help assess where your risks lie and to ensure you are doing all you can do to keep you and your business secure.
Look out for our ‘Cyber Tip Tuesday’ video blog and on our YouTube channel.
You can also follow us on Facebook, Twitter and LinkedIn.
Links to external articles are provided for general interest and awareness only. Linking to or reposting external content does not constitute endorsement of or by any organisation, service, or product. We do not control and are not responsible for the content, security, or availability of external websites or links. Full credit is given to the original authors and sources. E&OE.